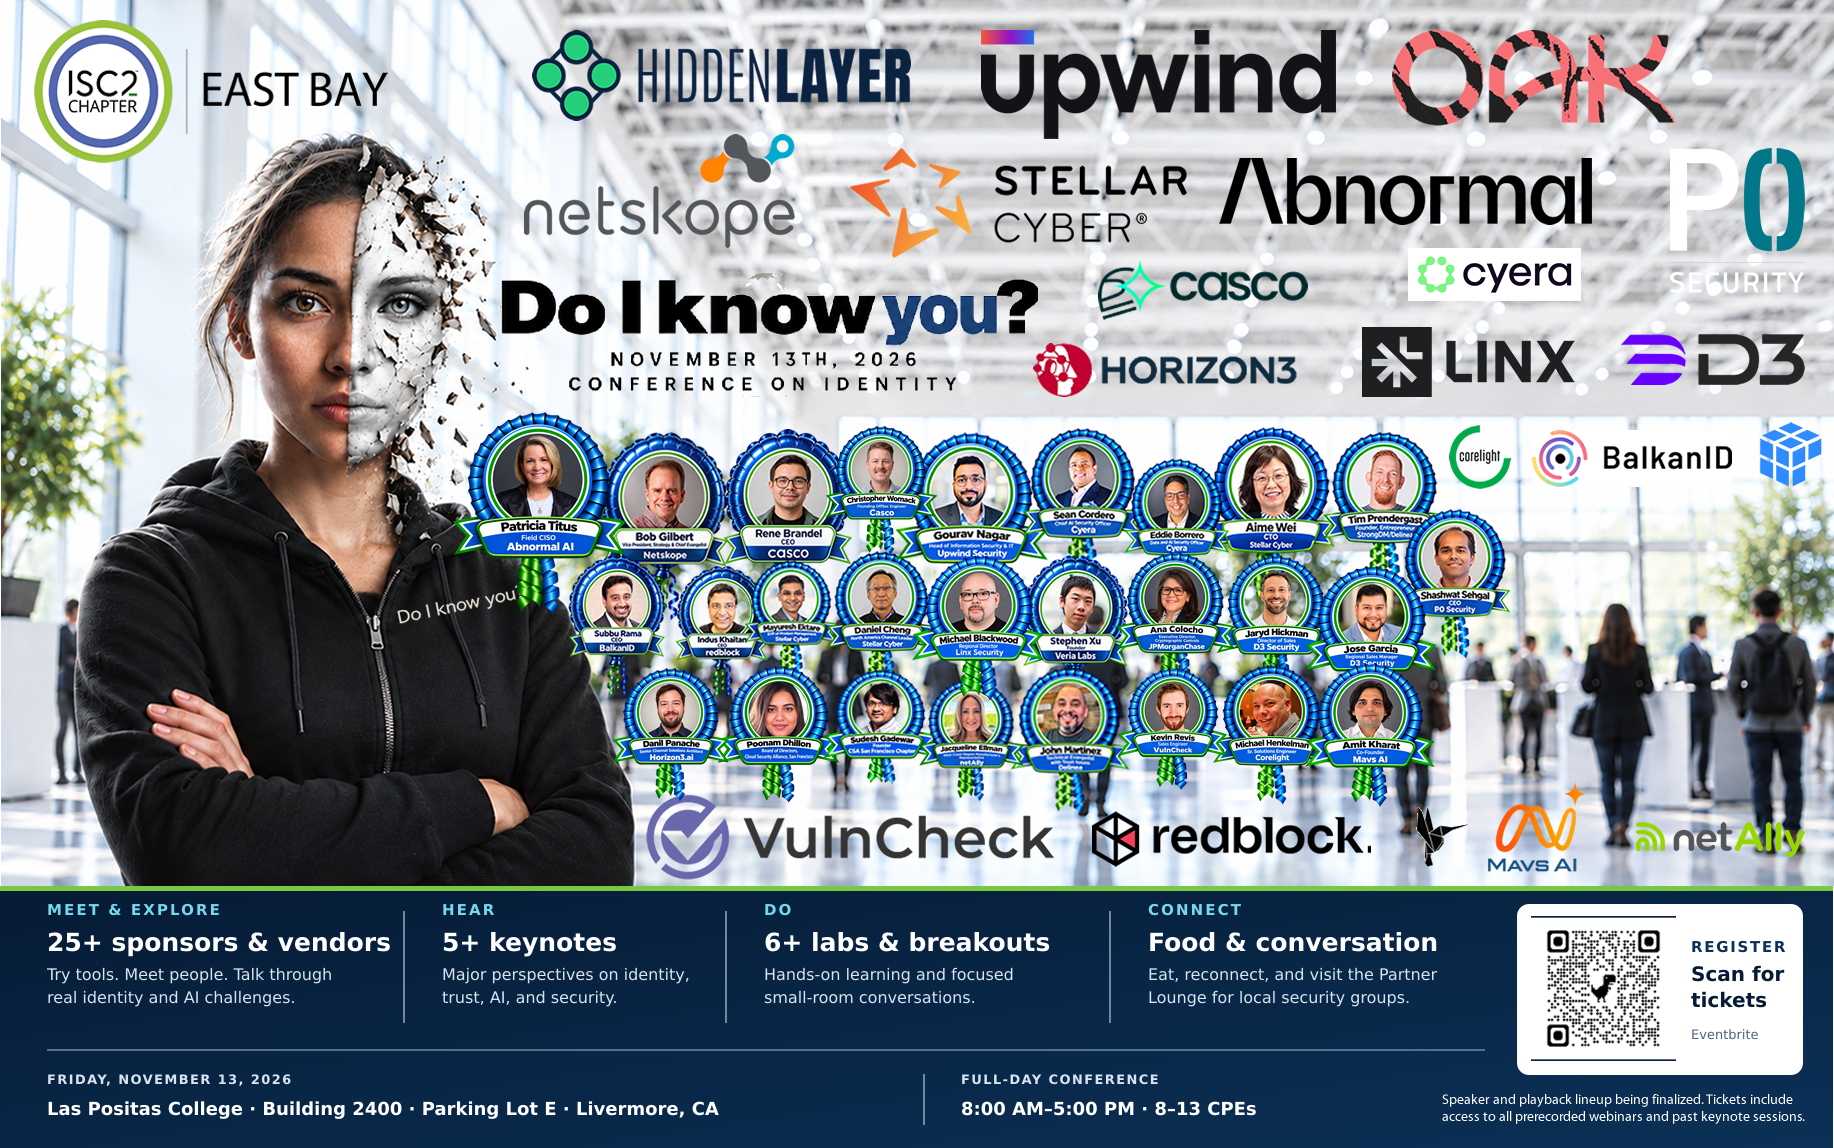
Do I Know You? Conference focus:
Modern identity now includes people, service accounts, APIs, machine workloads, autonomous agents, and the systems that grant them authority. Do I Know You brings the East Bay cybersecurity community together to examine how organizations can verify identity, govern access, detect abuse, and preserve trust across human and non-human environments.
- Non-human and AI agent identities, including service accounts, workload identities, and API keys
- Identity threat detection and response for credential abuse, session hijacking, and privilege escalation
- Zero Trust IAM architecture, continuous authentication, and dynamic access controls
- Biometrics, synthetic identity, deepfakes, and identity-centered social engineering
- Practical identity alignment with OWASP guidance for LLM and agentic AI security
Conference experience
The day combines main auditorium keynotes, flexible technical breakouts, demonstrations, question-and-answer sessions, panel discussions, an exhibition area, a Partner Lounge, and structured networking. Full breakfast, a networking lunch, and an afternoon cake break are included in the day.
Recorded playback access will be available for selected sessions. Don’t worry if you miss a favorite presenter. QR codes to attend their future and past webinars are provided at every vendor station. Attendees may earn up to 13 CPEs through the combined live and playback program.
Although we tried to find space for all of our sponsors, some vendors are allocated to the March Conference, Debt Collector, due to improved alignment between their core offering and the theme of our learning.
| Conference information | Details |
|---|---|
| Date | Friday, November 13, 2026 |
| Conference hours | 8:00 AM–5:00 PM PST; event setup begins at 7:30 AM |
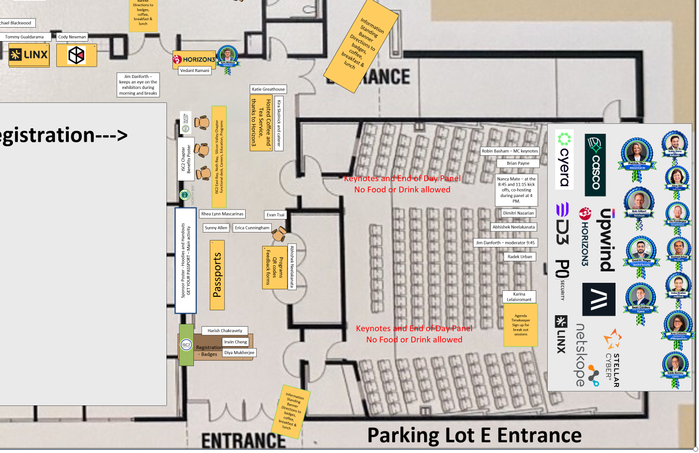
| Venue | Las Positas College, Building 2400, Parking Lot E, Livermore, CA, and outdoor weather-resilient tented campus grounds, Livermore, California |
| CPE credits | 8 CPEs for full-day live attendance plus up to 5 CPEs through recorded playback access Volunteers and Speakers earn up to 5 additional CPEs |
| Audience | 175–250 cybersecurity practitioners, CISOs, GRC leaders, entrepreneurs, industry leaders, and student scholars |
Distinguished Speaker Dinner – By Invitation Only (check your ticket for a coupon link)
| Date and time | Thursday, November 12, 2026, 5:00 PM to 8:30 PM |
| Location | McKay’s Beer Garden, Pleasanton, California |
| Hospitality | Dinner and open bar |
| Attendees | Keynote speakers, Platinum, Gold, and Silver sponsor representatives, Chapter Board members, invited CISOs, VIP guests, and ticketed members – you must buy a ticket, either conference or dinner, or be a paid sponsor. Remember, as a charity, ticket sales go directly to supporting students and educational activities. *Speakers, sponsors, and committee members will have their dinner invitation sent to them directly. |
| Purpose | VIP networking, speaker alignment, pre-conference briefing, and relationship development with prospective partners for the March 2027 conference |
Our mission of shared stewardship
The ISC2 East Bay Chapter is incorporated as a nonprofit public benefit corporation under Internal Revenue Code section 501(c)(3), EIN 47-1242819. We view our sponsors as collaborative defense partners whose support funds student scholarships, workforce development, and local community education.
| Category | Base Ticket | Ticket + Hoodie Add-On | Sizing & Requirements |
| ISACA, ISC2, ISSA, CSA, Pacific Hackers | Reciprocal chapter codes are communicated to your chapter leaders. Using the code in the registration releases member pricing. ISC2 East Bay members use their email as their code. | ||
| Dues-Paying Chapter Members | $145 | $170 | Unisex Sizing (S, M, L) |
| After 10/31/2026 – Non-Member Guests | $175 | $200 | Unisex Sizing (S, M, L) |
| Students, Retirees, Unemployed | $75 | $100 | Hoodie size is not guaranteed Unisex Sizing (S, M, L) |
Conference agenda
| Time | Main program | Concurrent activity or status |
| 7:30 – 8:00 AM | Event setup and logistics readiness | Breakout rooms, tents, exhibitor stations, and staff setup |
| 8:00 – 8:45 AM | Registration and breakfast | Networking, booth visits, coffee, and breakfast service |
| 8:45 – 9:00 AM | Welcome and opening remarks | Robin Basham, Conference Chair – Introducing your committee and 2026 ISC2 East Bay Board |
| 9:00 – 9:45 AM | Keynote: The Enemy Inside the Org Chart: Stopping Fake Employees & Synthetic Workforce Infiltration | Patricia Titus, Field Chief Information Security Officer at Abnormal AI |
| 9:45 – 10:15 AM | See the day’s preview below | Guiding your choices for an impactful day |
| 10:15 – 10:45 AM | Morning coffee and networking break | Exhibition area and vendor SME conversations |
| 10:45 – 11:30 AM | Keynote: The Two Sides of AI in Cybersecurity | Bob Gilbert, Vice President of Strategy and Chief Evangelist, Netskope – expanding on the incredible arc of conversation across 2026, we’re going to examine what we’re finding in real time in enterprises across the United States and beyond. |
| 11:30 AM – 12:15 PM | Keynote: Runtime Is The Truth | Steve Szymczak, Solutions Architect will be standing in for Gourav Nagar, Head of Information Security and IT, Upwind Security |
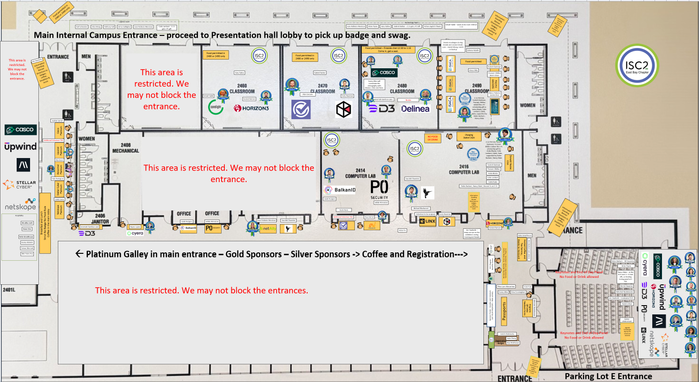
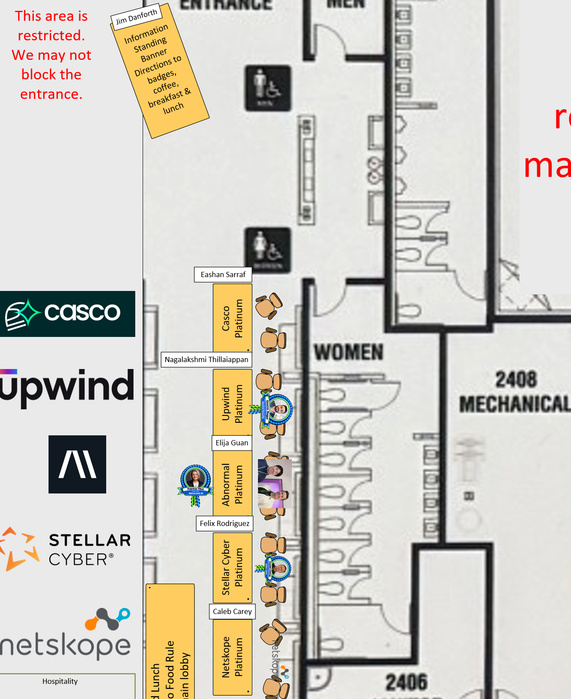
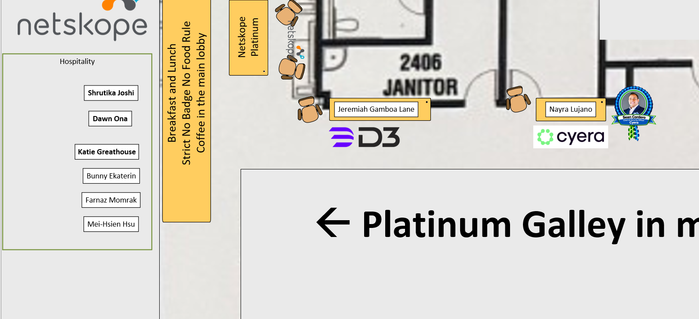
| 12:15 – 12:45 PM | Networking lunch | Expo and Partner Lounge – food served in the Platinum Galley with the option to visit rooms 2460, 2470, 2480, and 2490 with food and drink. |
| 12:45 – 1:30 PM | Fireside Chat: Continuous autonomous testing and guardrails | Rene Brandel, CEO, Casco; Partner Lounge networking room 2480 |
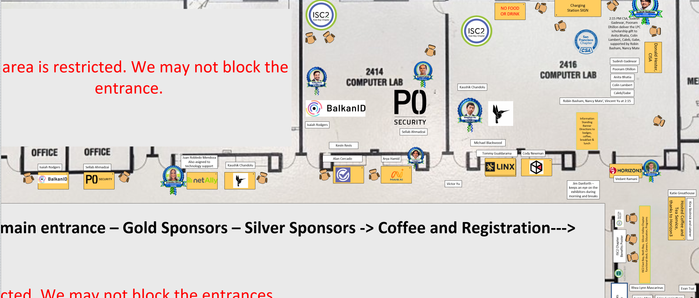
| 1:30 – 2:15 PM | Flexible breakout block one | Room 2414: BalkanID, Subbu Rama – Hunt the Ghosts: Finding Risky Identities Before Attackers Do (Including Your AI Agents) Room 2460: Corelight, Michael Henkelman – Unauthorized Tool Execution Room 2470: VulnCheck, Kevin Revis – From CVE Lists to Adversary Reality Room 2480: D3 Security, Jaryd Hickman – Morpheus and the Future of the SOC |
| 2:15 – 3:00 PM | Flexible breakout block two | Room 2414: P0 Security, Neha Duggal – Your AI Agent Has Permission. Should It? Room 2460: Horizon3.ai, Danil Panache – Stochastic Intent, Deterministic Action Room 2470: Redblock.ai, Indus Khaitan – AI Meets Cyber: An Open Q&A with a Founder and an AI Engineer Room 2480: Delinea, John Martinez – Just-in-time Works For AI Too Room 2490: CSA SF, Poonam Dhillon and Sudesh Gadewar – Awarding the LPC Cyberclub with a financial gift; Would you let them in? The Identity Decision Game & The Identity Handoff |
| 3:00 – 3:30 PM | Cake break, expo visits, and vendor Q&A | Exhibition Hall and vendor SME conversations – Coffee and cake supplied by Horizon3 |
| 3:30 – 4:00 PM | Keynote: The Next Breach Will Be Authorized: Why Allowed Is Not the Same as Safe | Sean Cordero, Chief AI Security Officer, Cyera |
| 4:00 – 4:50 PM | CISO and Cyber Leaders panel | The array of CTOs, CEO, and CISOs is quickly expanding. Sean Cordero will moderate an exciting and fast-paced view of what we must be doing with AI right now, using, defending, rearchitecting, and rethinking: Do I know you? Confirmed so far: Shashwat Sehgal, Aime Wei, Eddie Borrero, Indus Khaitan, Subbu Rama, Ana Colocho, and open invitations to all Platinum keynotes |
| 4:50 – 5:15 PM | Closing remarks, vendor gift giveaways. Conference Feedback & CPE distribution | Closing assembly in the main auditorium; teardown follows from 5:00 to 5:30 PM Form: Mandatory Conference Feedback Form |
Featured Platinum speakers and session leaders
Keynote Abnormal: The Enemy Inside the Org Chart: Stopping Fake Employees & Synthetic Workforce Infiltration
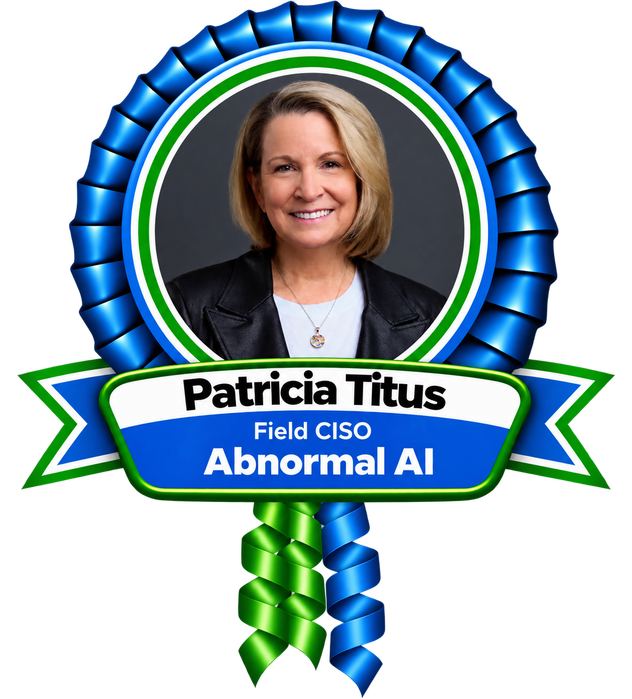
With over 25 years of experience as a cybersecurity leader, Patricia Titus now leads as Field Chief Information Security Officer at Abnormal AI. Her extensive background includes CISO positions at prominent organizations such as Booking Holdings, Markel Corporation, Freddie Mac, Symantec, Unisys, and the Transportation Security Administration. Throughout her career, she has been responsible for developing and implementing security strategies that align with business objectives and ensure adherence to global regulations. Recognized for her expertise in areas like risk management, artificial intelligence, cybersecurity operations, and crisis management, Patricia has a proven track record of optimizing security frameworks, improving business resilience, and incorporating innovative solutions, including AI, into security practices. She currently contributes her expertise by serving on the boards of Black Kite, The Girl Scouts of the Commonwealth of Virginia, and Glasswing Ventures.
Abnormal AI (abnormal.ai) is the leading AI-native human behavior security platform, leveraging machine learning to stop sophisticated inbound attacks and detect compromised accounts across email and connected applications. The anomaly detection engine leverages identity and context to understand human behavior and analyze the risk of every cloud email event—detecting and stopping sophisticated, socially engineered attacks that target human vulnerability.
Keynote Netskope: The Two Sides of AI in Cybersecurity
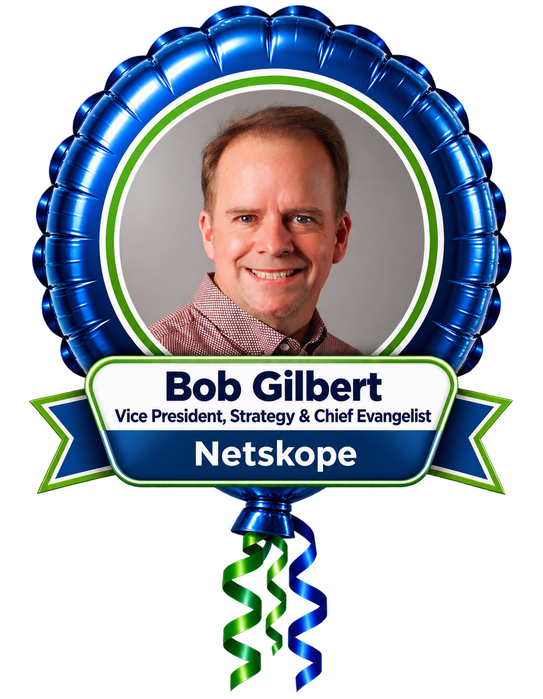
Bob Gilbert is the Vice President of Strategy and Chief Evangelist at Netskope, a market-leading cloud security company. Bob is a prolific speaker and product demonstrator, reaching live audiences in more than 45 countries over the past decade. His career spans more than 25 years in Silicon Valley, where he has held leadership roles in product management and marketing at various technology companies. He was formerly the Chief Evangelist at Riverbed, where he was a member of the pioneering product team that launched Riverbed from a small start-up of less than 10 employees to a market leader with more than 3,000 employees and $1B in annual revenue.
Bob was first introduced to the world of cybersecurity as a teenager in the 80s when he hosted a BBS and had to develop his own terminal software to prevent Russian hackers from infiltrating his site, which was being hosted from his parents’ home.
Netskope (netskope.com) is a leader in modern security, networking, and analytics for the cloud and AI era. The unique architecture of its Netskope One platform enables real-time, context-based security for people, devices, and data wherever they go, and optimizes network performance—without trade-offs or sacrifices. Thousands of customers and partners trust the Netskope One platform, its patented Zero Trust Engine, and its powerful NewEdge Network to reduce risk, simplify converged infrastructure, and provide full visibility and control over cloud, AI, SaaS, web, and private application activity.
Keynote Upwind: Runtime Is The Truth
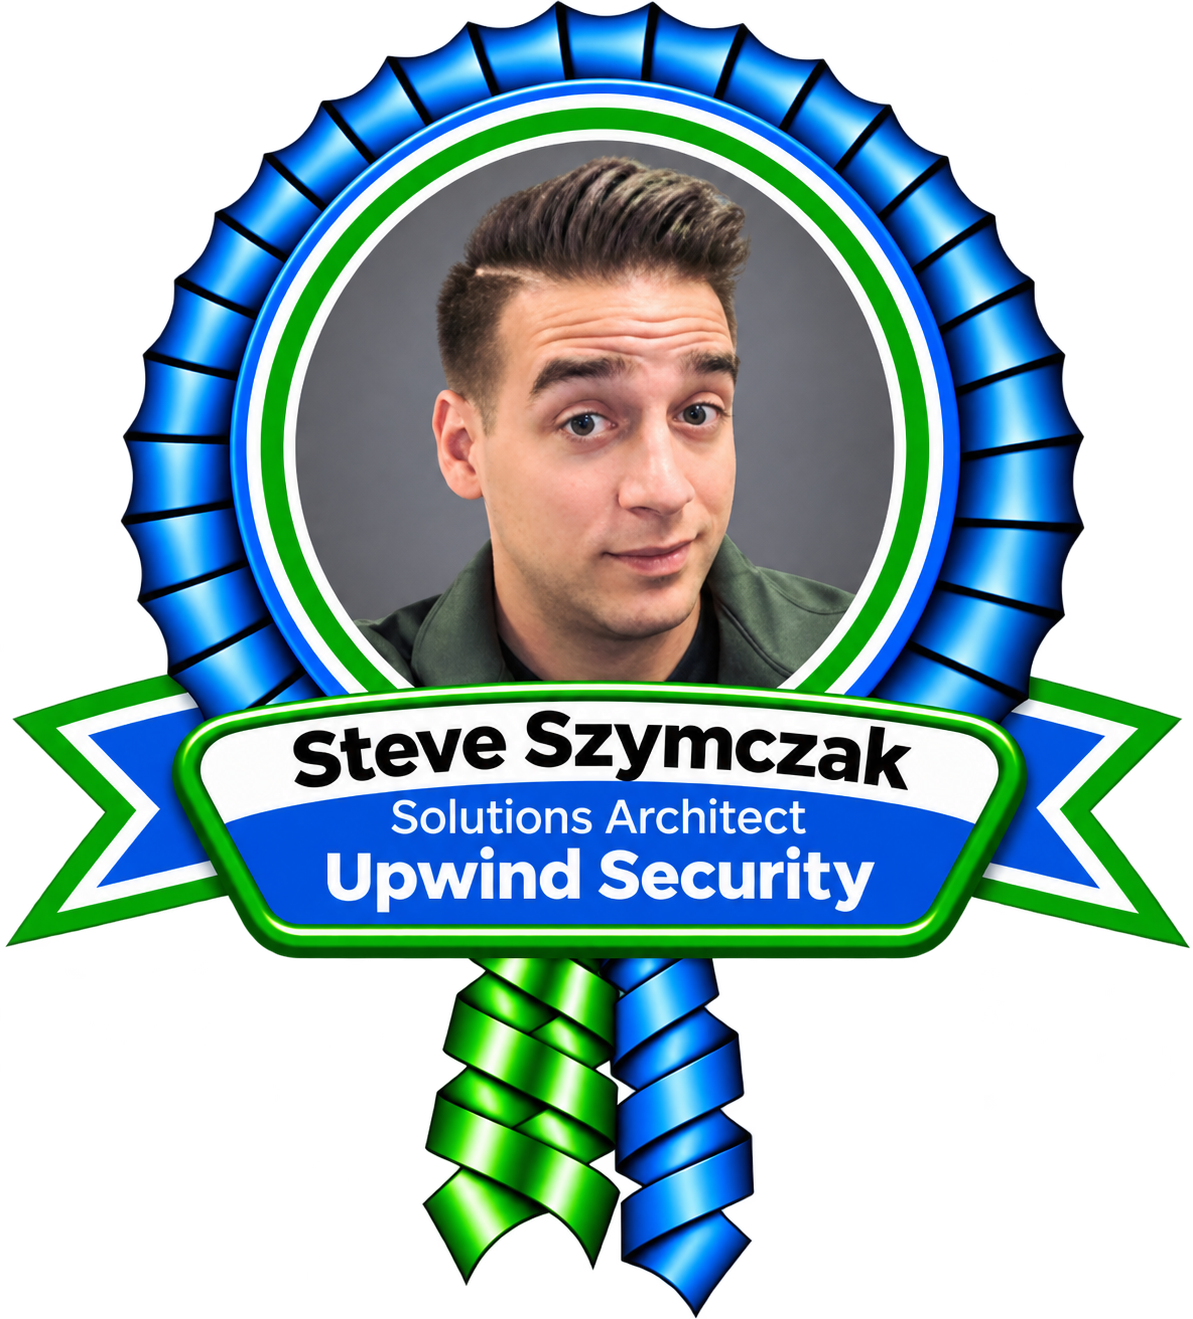
Steve Szymczak is a Solutions Architect at Upwind Security, helping organizations secure cloud and AI workloads through runtime-driven visibility and threat detection. Over more than a decade, Steve has worked across the infrastructure stack, from troubleshooting data center networks as a Cisco TAC engineer to designing hyperconverged solutions at Nutanix, advising on enterprise security at IBM, and guiding cloud security strategy at Wiz and Upwind. A graduate of Rochester Institute of Technology (RIT), Steve is known for turning complex technology into clear, practical business outcomes.
Upwind Security (upwind.io) delivers a runtime-powered Cloud-Native Application Protection Platform that unifies application security, cloud security posture, and real-time protection on a single platform. Instead of relying on static configuration scanning, Upwind pairs agentless cloud scanning with lightweight eBPF runtime sensors to observe how workloads actually behave in production at the process, network, and system call level, then uses that live context to rank findings by real exploitability rather than theoretical severity. The platform spans posture management, attack path analysis, vulnerability management, entitlements, container and Kubernetes security, data security posture management, API security, and cloud detection and response, alongside an AI security suite covering AI posture management, AI detection and response, and AI bill of materials for teams moving models into production. Founded in 2022 by the team behind Spot.io and headquartered in San Francisco, Upwind helps security teams cut alert noise and shorten the distance between finding a risk and fixing the one that matters.
Luncheon catered by Morucci’s served in the Partner Lounge and all along the Platinum Galley, followed by a fireside chat.
Sandwiches: Veggie Delight, Chicken Pesto and Tri-Tip * Salads: Caesar, House * Soups: Chicken Tortilla, Italian Wedding * Desserts: An assortment of cookies and bars (lemon, peanut butter, raspberry coconut, and brownies)
Keynote Casco: Continuous autonomous testing and guardrails – a fireside chat with René Brandel and Chris Womack, starting at 12:30 in room 2480. Please bring your lunch and settle in.
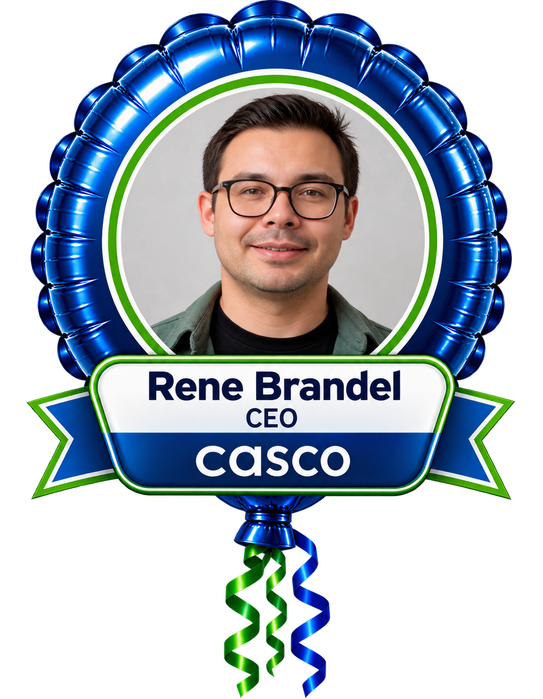
René Brandel is the Founder & CEO of Casco, an AI-native security company providing always-on, autonomous red-teaming and security testing across web apps, APIs, infrastructure, and AI systems. Casco recently raised a Series A at a $100M valuation led by Standard Capital/Y Combinator and became the first All-American Agentic Offensive Security tool listed on the FedRAMP Marketplace.
Prior to founding Casco, René was Head of Product at Amazon Web Services (AWS), where he created Kiro—one of the fastest-adopted IDEs in history (100,000 developers within three days)—and led AWS Amplify Gen 2. He also served as a Program Manager at Microsoft, leading cross-platform intelligence SDKs and developer integrations across Teams, Skype, and Office.
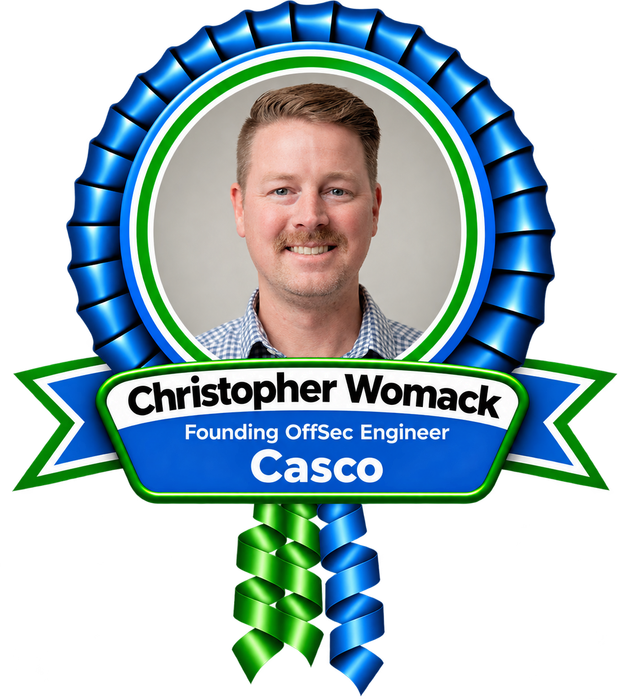
Chris Womack helps enterprises and federal organizations reduce cyber risk through Casco’s offensive security platform. His work focuses on helping organizations identify exploitable vulnerabilities, validate risk at runtime, and reduce engineering time spent on triage and remediation.
Previously at AWS, Chris worked on AI products and developer tools, helping bring Kiro, AWS’s agentic IDE, to market. His background spans cloud application development and the use of AI agents to build software.
Casco (casco.com) provides autonomous security testing for web applications, APIs, infrastructure, and AI systems. Moving beyond traditional, intermittent penetration testing, Casco offers “always-on” security that integrates directly into the development lifecycle. The platform utilizes advanced intelligence to identify critical vulnerabilities, such as broken object-level authorization and prompt injection. Every finding is safely exploited to prove its business impact. Casco also allows users to one-click retest and generate code fixes for every finding. Casco is trusted by over 250 companies, from high-growth startups like CrewAI to large enterprises like Gusto. As a Gold Sponsor of OWASP AI Exchange, Casco is committed to advancing AI-driven security standards for the global developer community.
Afternoon breakout sessions – meet legacy Platinum, Gold and Silver Sponsors – Earn extra CPE by registering for their past and future ISC2 East Bay Chapter webinars
BalkanID – Live Session with Subbu Rama
Hunt the Ghosts: Finding Risky Identities Before Attackers Do (Including Your AI Agents)
– Room 2414, 2:15 PM –
Every environment has ghosts: former employees who still have access, service accounts with keys that have not been rotated in years, and accounts no one can map to a real person. Now a new kind is appearing. AI agents are being created across the enterprise with credentials and entitlements, but often with no owner, no approval, and no review.
This session walks through the most common identity ghosts found in real enterprise environments, how attackers exploit them, and how to hunt them down systematically. It closes with how to apply proven governance controls (approval at creation, accountable ownership, least privilege, periodic review, and clean decommissioning) to AI agents before they become your next blind spot.
Attendees will leave with a practical checklist to find and eliminate the ghosts in their own environment, mapped to NIST, SOC 2, and CISSP Domain 5.
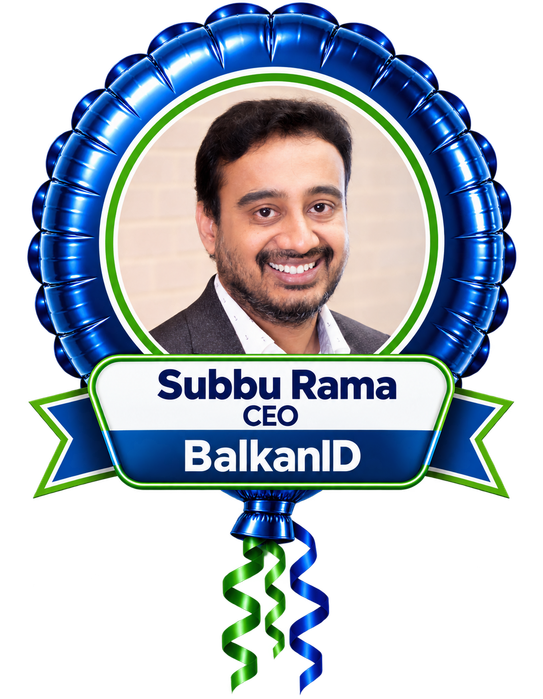
Subbu Rama is a 3x founder and the CEO and Co-founder of BalkanID, a company specializing in identity security access governance solutions. With close to 2 decades in the tech industry, he has a strong background in infrastructure, AI, cybersecurity, and cloud computing, holding product, engineering, and cybersecurity roles. Prior to BalkanID, Subbu co-founded Bitfusion, a startup focused on virtualization technologies for AI and GPU infrastructure, which was later acquired by VMware (Dell Technologies). He is passionate about building innovative solutions that tackle complex challenges. Subbu holds a Master’s degree in Electrical and Computer Engineering from the University of Wisconsin-Madison and is an Early Career Award Recipient.
Watch Subbu Rama’s presentation on Identity Security in the Age of AI Agents: Beyond Traditional IGA from the June 2026 member meeting.
BalkanID (balkan.id) provides modular, AI-assisted identity security and access governance (IGA) solutions designed to work with both connected and disconnected applications. Its platform streamlines critical tasks such as user access reviews, lifecycle automation with purpose-based just-in-time access, and identity security posture management (ISPM)—including IAM risk and RBAC analysis and an AI Copilot feature. By empowering organizations to enforce least privilege principles, BalkanID enables enterprises to efficiently manage complex identity risks at scale.
D3 Security – Live Session with
Jaryd Hickman & Jose Garcia
Morpheus and the Future of SOC
– Room 2480, 1:30 PM –
Jaryd Hickman leads sales and sales development at D3 Security, bringing over a decade of cybersecurity sales experience to the team. His background spans enterprise security solutions across DLP, NGFW, cloud security, email security, and managed detection and response. Jaryd is based in Austin, Texas.
D3 Security builds Morpheus, the accountable agentic AI SOC platform that investigates every alert and tells its story: what happened, whether you’re at risk, and what to do. Morpheus triages and L2-investigates up to 95% of alerts in under two minutes, reconstructing the attack path across EDR, identity, email, cloud, and network. Four autonomy modes, 800+ self-healing integrations, and one unified audit trail per incident keep a human in command of every consequential action. Trusted by Fortune 500 enterprises, governments, and the world’s largest MSSPs.
Redblock.ai – Live Session with Indus Khaitan
AI Meets Cyber: An Open Q&A with a Founder and an AI Engineer
– Room 2470, 2:15 PM –
followed by participation on the end-of-day panel at 4 PM
Ask a founder and an AI engineer anything:
- AI in security, careers, startups, and what’s real versus hype.
- How do you build an AI agent you’d trust with production access? Come ask.
- Breaking into AI security? Bring your questions about skills, tools, and what teams look for.
- When AI agents outnumber employees, who governs their access? Come ask.
- Will IGA as we know it survive the AI agent era? Come argue about it.
Indus Khaitan is CEO and founder of Redblock, an AI automation startup dedicated to eliminating the repetitive ‘eye on the glass’ work performed by cybersecurity teams. Previously, Indus co-founded BitzerMobile, a mobile security company acquired by Oracle. He holds a degree in computer science from the Birla Institute of Technology, Mesra, and lives in the San Francisco Bay Area.
Redblock (redblock.ai) automates identity and security workflows across disconnected apps — extending SailPoint and other identity systems for full coverage. It connects what Identity systems can’t, eliminates CSVs and IT tickets, and automates actions safely with policy guardrails. The result: a smaller identity attack surface in days, not months. Manual workflows become autonomous, auditable actions.
Horizon3.ai – Live Session with Danil Panache
Stochastic Intent, Deterministic Action; Where AI reasoning ends, and attack execution begins
– Room 2460, 2:15 PM –
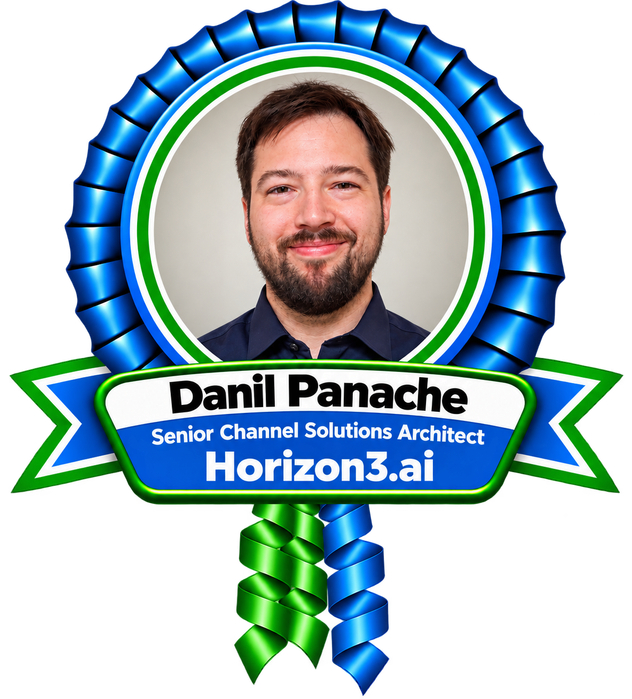
Danil Panache is a Senior Channel Solutions Architect at Horizon3.ai, focused on continuous autonomous penetration testing. With over a decade of experience in cybersecurity, including threat intelligence, security engineering, and working directly with SOC and CSIRT teams, Danil brings a practitioner’s perspective on both offensive techniques and the defensive realities organizations face.
Horizon3.ai (horizon3.ai) provides NodeZero, an autonomous penetration testing platform. It continuously assesses an organization’s internal and external attack surface, automatically discovers exploitable weaknesses, and verifies vulnerabilities without human intervention. By rigorously emulating real-world attacker behaviors and techniques, NodeZero identifies critical attack pathways and provides clear, actionable remediation steps to proactively strengthen security posture and continuously validate an organization’s defenses against evolving cyber threats, supporting a continuous security validation program.
Delinea – Live Session With John Martinez
Just In Time Works for AI Too
– Room 2480, 2:15 PM –
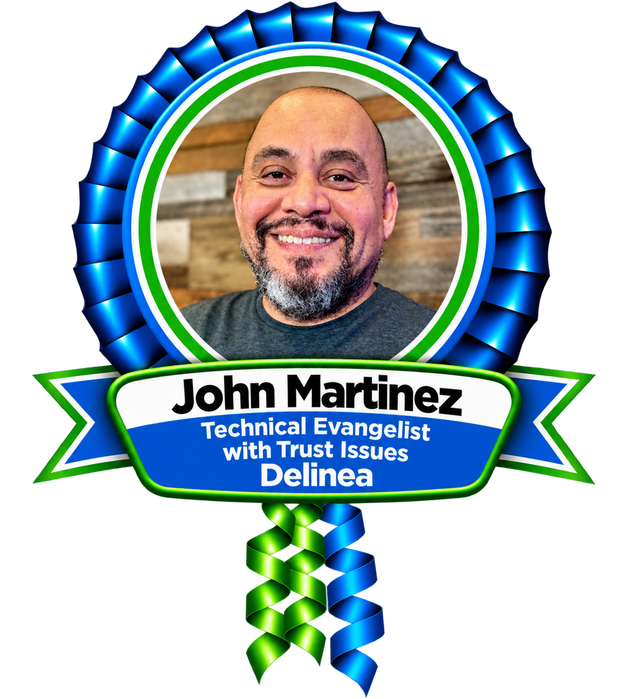
John Martinez is a Technical Evangelist at Delinea and a long-time security practitioner who has worn many hats over the years. Before Delinea, he worked in the Cloud Security space in Engineering and Customer-facing roles at Palo Alto Networks and Evident.io, where CSPM was created. Before that, he was a cloud security and operations practitioner at Adobe and Netflix.
Mavs.ai – Enjoy the amazing playback session: GenAI Runtime Security, Mavs AI. Visit with Amit in front of Room 2414
For the first time in security history, employees are routinely sending sensitive data to third-party systems and calling it productivity. Join us for a technical deep-dive into why the prompt layer is your new attack surface, why legacy DLP and CASB fail here, and what runtime in-loop security actually looks like, covering sensitive data exposure, prompt injection, jailbreaks, and agentic AI threats mapped to OWASP LLM Top 10. Closing with a Mavs AI runtime security demo.
GenAI Runtime Security_Webinar_20261008_v1.0Download
Amit Kharat is a cybersecurity entrepreneur and co-founder of Mavs AI, building next-generation runtime security for Generative AI use. With over a decade of experience in data-centric and enterprise security, Amit has played a foundational role in scaling global security platforms across BFSI, manufacturing, pharma, and government sectors. His work spans product strategy, go-to-market leadership, and deep customer engagement across North America, Europe, the Middle East, and India. At Mavs AI, Amit is focused on solving emerging GenAI risks, including sensitive data exposure, prompt-level attacks, and lack of runtime visibility, helping enterprises adopt AI with confidence and control.
About Mavs AI
Mavs AI (mavsai.com) is on a mission to help enterprises embrace Generative AI confidently by addressing the unique risks of a LLM / model-driven world. As organizations embed Large Language Models (LLMs) into day-to-day workflows, Mavs AI delivers real-time, in-the-loop security by monitoring every interaction to detect and prevent the leakage of sensitive data, such as PII and IP. Our LLM-agnostic engine acts as a specialized security layer that intercepts and analyzes prompts and responses, identifying risks like prompt injection and data exposure before damage is done. By enforcing policies across users, agents, and applications, Mavs AI enables organizations to maintain strict governance over their AI ecosystems without compromising performance. In an era where GenAI is transforming global productivity, Mavs AI ensures that this transformation happens securely, responsibly, and at scale.
Mavs AI delivers smart guardrails, intelligent policy control, and real-time visibility for every GenAI interaction. They address specific risks like PII and sensitive data shared in prompts, prompt injections compromising systems, and misuse by business users or rogue application users. Mavs AI closes the gap where innovation outpaces safety guardrails, enabling enterprises to innovate fearlessly and scale AI responsibly.
NetAlly – Hands-on portable network testing device
NetAlly (netally.com) offers portable network testing and analysis solutions essential for IT and cybersecurity professionals managing complex infrastructures. Its suite of tools provides deep visibility into both wired and wireless networks, enabling efficient troubleshooting of connectivity issues, precise validation of network performance, and verification of security configurations. This comprehensive approach helps ensure reliable network infrastructure, reduces downtime, and facilitates rapid issue resolution for enhanced operational stability and secure network operations.
P0 Security – Live Session with Neha Duggal
Your AI Agent Has Permission. Should It?
– Room 2414, 2:15 PM –
An AI agent receives a legitimate request, authenticates successfully, and takes an action it’s fully authorized to perform. There’s just one problem: it’s the wrong action.
Traditional identity and access management was never designed for machines that make thousands of decisions a day, often using permissions far broader than the task requires. And quarterly access reviews aren’t going to fix that.
What if access controls could learn from actual behavior, recommend better policies, and make smarter decisions before an agent acts?
In this session, Neha will explain how continuous access analytics, human-approved policies, and runtime enforcement can work together to close the gap between what an agent can do and what it should do. You’ll leave with a practical approach to identifying excess access, reducing risk and getting started with one agent in your own environment.
Neha previously presented to the chapter this year. You might enjoy listening to her recent presentation: Are you modernizing your tool stack? – P0 SecurityDownload
Neha Duggal is an accomplished product leader with deep expertise in cloud security, observability, and enterprise SaaS. With more than 15 years of experience, she has led multiple products from early concept to wide-scale customer adoption, built high-performing cross-functional teams, and driven product strategies that delivered measurable business outcomes. Known for her strong technical grounding and collaborative leadership style, Neha excels at simplifying complex problems, aligning stakeholders, and executing at scale. She has a track record of launching differentiated security capabilities, improving product-market fit, and guiding organizations through periods of rapid growth and transformation. Neha is passionate about building products that deliver real customer value, elevating product excellence within organizations, and mentoring the next generation of product leaders.
P0 Security – Shashwat Sehgal – 4 PM Panel
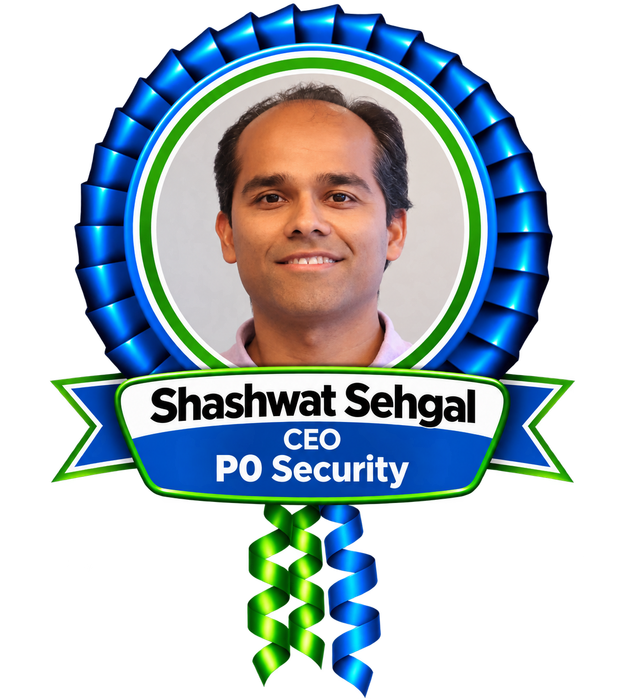
Shashwat Sehgal is the Founder and CEO of P0 Security, re-architecting Privileged Access Management (PAM). He specializes in automating access for the “identity explosion” within production stacks. Previously, at Splunk, he led OpenTelemetry initiatives for microservices, and at Cisco Meraki, he used ML for automated network troubleshooting. He is an IIT-Delhi and Columbia Business School graduate.
Watch Shashwat Seghal’s presentation Are you modernizing your identity tool stack? from the February 2026 member meeting.
P0 Security (p0.dev) is helping companies modernize PAM for multi-cloud and hybrid environments with the most agile way to ensure least-privileged, short-lived, and auditable production access for users, NHIs, and agents. Centralized governance, just-enough-privilege, and just-in-time controls deliver secure access to production, as simply and scalably as possible. P0’s Access Graph and Identity DNA data layer make up the foundational architecture that powers privilege insights and access control across all identities and production resources, including the new class of AI-driven agentic workloads emerging in modern environments.
Stellar Cyber – Enjoy real-time conversations with Daniel and Mayuresh – Meet CTO Aime Wei during the afternoon panel
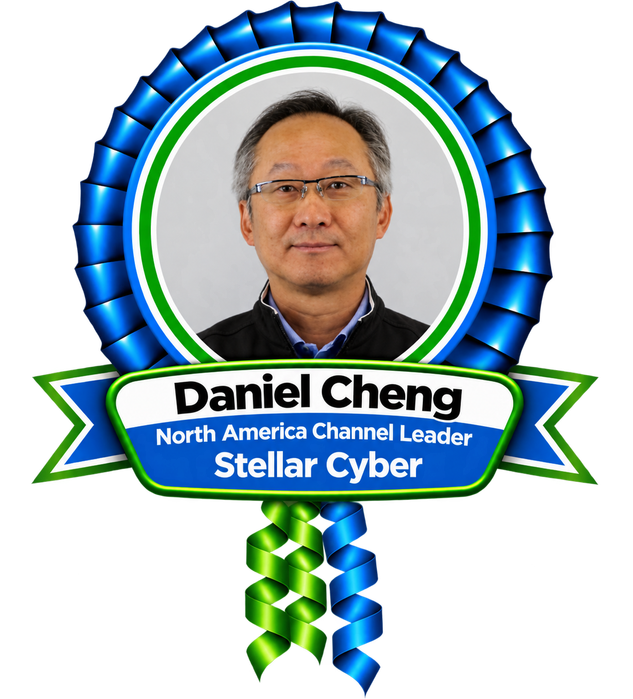
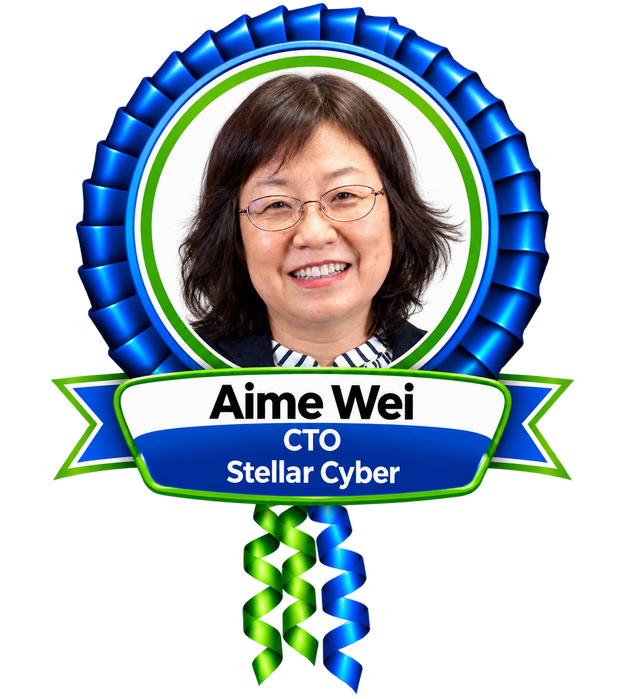
Daniel Cheng is the Head of North America Channel at Stellar Cyber, where he leads the strategy and execution of the company’s reseller ecosystem. With a strong focus on enablement, trust, and execution, Daniel works closely with partners to help them successfully adopt and scale Stellar Cyber’s AI-driven SecOps platform. Since taking on this role in early 2025, Daniel has played a key role in expanding channel awareness, developing a growing community of technical champions, and strengthening partner capabilities through certification and hands-on training. His work bridges business strategy and technical execution, ensuring partners are equipped to deliver real value to their customers. At the ISC2 East Bay Conference, Daniel will serve as Stellar Cyber Lab Leader, guiding participants through an interactive, hands-on session that demonstrates how a unified, open, and AI-powered SecOps platform can simplify threat detection, investigation, and response while improving operational efficiency and security outcomes.
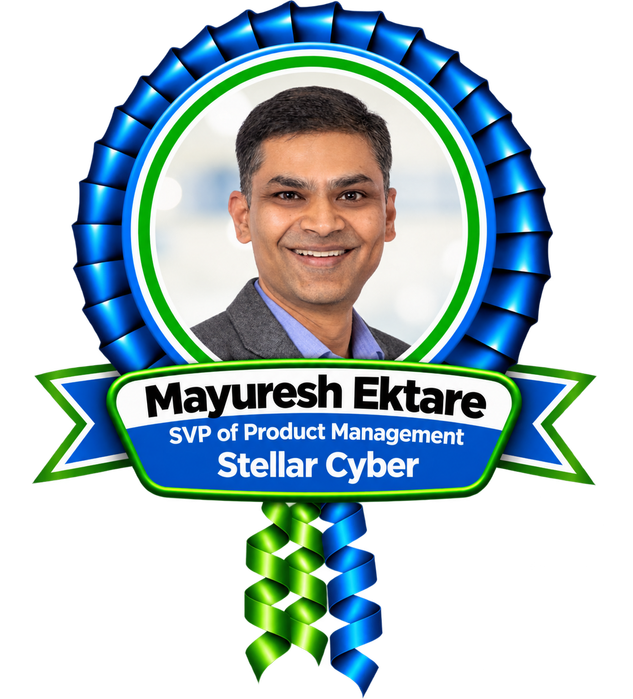
Mayuresh Ektare, Senior Vice President, Product Management
Mayuresh is a seasoned product management executive with over 20 years of experience building category-defining cybersecurity platforms. He operates at the intersection of business strategy, product vision, and technology, with a strong track record of scaling organizations and driving product transformations.
Prior to Stellar Cyber, he served as VP of Product Management at Qualys, where he led the organizational transformation from vulnerability scanning to an agentic AI-driven Exposure & Risk Management platform. Previously, as SVP at Brinqa, he helped establish leadership in Risk Operations, and as a founding member of Zingbox, he built and scaled an IoT security solution from its inception through its acquisition by Palo Alto Networks. He also held leadership roles at Aerohive Networks and Trend Micro. Mayuresh holds several patents in cybersecurity and has a master’s degree in Industrial Engineering from Clemson University.
Aimei Wei has more than 20 years of experience building successful products and leading teams in data networking and telecommunications. She has extensive experience working for both early-stage startups, including Nuera, SS8 Networks, and Kineto Wireless, as well as well-established companies like Nortel, Ciena, and Cisco. Prior to founding Stellar Cyber, she was actively developing Software-Defined Network solutions at Cisco. Aimei enjoys building a product from its initial design to its final launch. Aimei has an M.S. in Computer Science from Queen’s University in Kingston, Canada, and an Undergraduate degree in Computer Science from Tsinghua University of China.
Stellar Cyber (stellarcyber.ai) is the innovator of Open XDR, the only intelligent, next-generation security operations platform that provides high-fidelity detection and response across the entire attack surface. By unifying EDR, SIEM, and NDR into a single, AI-driven interface, Stellar Cyber eliminates the data silos that traditional security tools create, providing a comprehensive, correlated view of the entire threat landscape. The platform uses advanced machine learning and behavioral analytics to automatically detect sophisticated attacks, reduce alert fatigue for security analysts, and significantly accelerate incident response workflows through a single, integrated “pane of glass.”
VulnCheck – Live Session with Kevin Revis
From CVE Lists to Adversary Reality
– Room 2470, 1:30 PM –
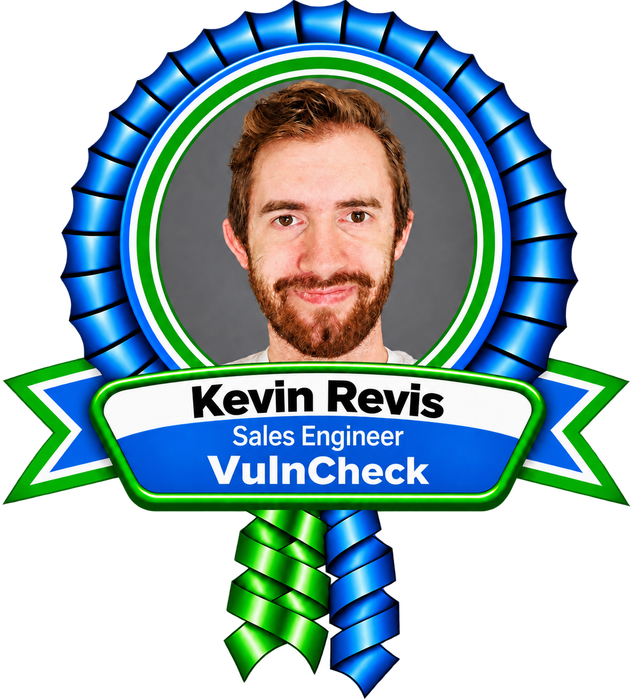
Kevin Revis, Senior Sales Engineer at VulnCheck and former Booz Allen Hamilton Technical Consultant, brings extensive expertise to discussions on vulnerabilities and AI. Holding a Master’s in Electrical and Computer Engineering from Purdue University and CompTIA Security+ certification, he specializes in bridging machine learning concepts with real-world cybersecurity solutions. Revis offers deep technical knowledge in vulnerability management, supply chain risk mitigation, and algorithmic risk assessments, combined with hands-on experience securing embedded systems and federal infrastructure. His background in translating complex ML, data science, and security frameworks into actionable defense strategies makes him a valuable resource for evaluating AI-driven security risks and intelligence.
Exploitation prevention is only as strong as the intelligence driving those efforts, and most of the industry is still running on intelligence that lacks exploit context. VulnCheck, The Exploit Intelligence Company, delivers structured exploit intelligence on what is actively weaponized in the wild, purpose-built for the data lakes, ETL pipelines, automation, and AI and LLM workflows your infrastructure already runs on, raising the capability of everything it powers.
Corelight – Live Session with Michael Henkelman
Unauthorized Tool Execution
– Room 2460, 1:30 PM –
Mike Henkelman is a Sr. Solutions Engineer for Corelight with thirty years of technical experience that includes building enterprise data centers and NOCs for ISPs, doing edge router and switch development for Cisco, and running the Vuln Management and FedRAMP IL5 programs for VMware. He frequently speaks at conferences such as DefCon and B-Sides.
Corelight (corelight.com) is the pioneer and fastest-growing provider of Open Network Detection and Response (NDR), delivering a unique approach to cybersecurity risk centered on comprehensive network evidence. As the only solution powered by the dual open-source foundations of Zeek® and Suricata—now enhanced by GenAI—Corelight provides deep visibility into network traffic by transforming raw data into high-fidelity logs, metadata, and actionable insights. By equipping elite defenders at the world’s most mission-critical enterprises and government agencies with this rich evidence, the platform enables rapid threat hunting, forensic analysis, and complete situational awareness across complex, distributed environments. Ultimately, Corelight helps security teams level up their defenses, accelerating investigations and dramatically reducing the time required to detect and neutralize sophisticated attacks and model theft.
CSA San Francisco Awards Scholarship, presented by Sudesh Gadewar and Poonam Dhillon to the LPC Cyber Club; Topic: Would you let them in? The Identity Decision Game; then, The Identity Handoff – When HR, IT and Security Don’t Connect?
Keynote: The Next Breach Will Be Authorized: Why Allowed Is Not the Same as Safe, Sean Cordero, Chief AI Security Officer, Cyera
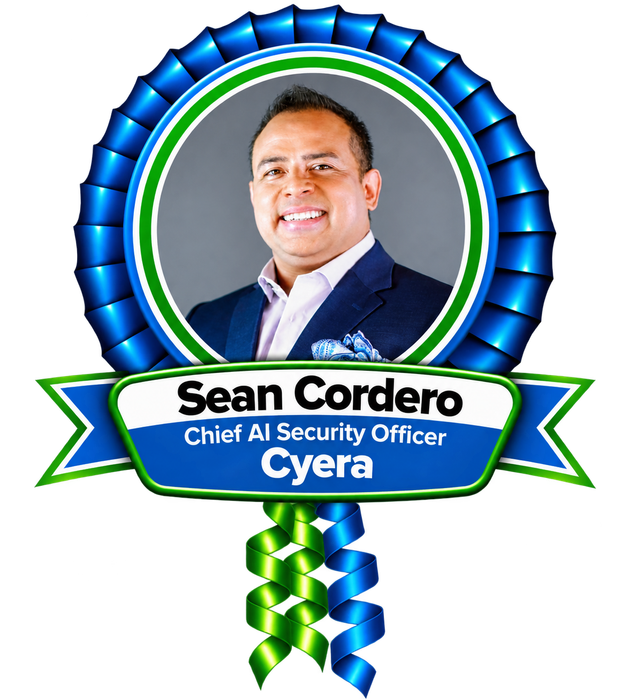
Sean Cordero is Chief AI Security Officer at Cyera, where he works with organizations to protect sensitive data as they adopt AI and autonomous agents. His career spans major shifts in enterprise technology, from cloud adoption to AI, with a consistent focus on protecting data. Sean’s work at Cyera focuses on helping organizations adopt AI securely, build trust into AI systems, and shape the standards that support both. He is also a Research Fellow with the Cloud Security Alliance (CSA) and a Certified CISSP.
Cyera (cyera.com) is building the trust layer powering enterprise AI transformation. Enterprises like Paramount, Chipotle, and Valvoline use Cyera to control exactly what data their AI can reach—and govern what happens next. The platform secures data at rest, in motion, and in use, whether touched by humans or AI agents. Valued at $12 billion and backed by over $2.3 billion from Accel, Blackstone, Cyberstarts, Georgian, Lightspeed, and Sequoia. Protect your data. Secure AI.
4:00 PM – The Final Panel: Six Industry Leaders Share a Moderated Conversation on Identity in the Age of AI
.
Partner Lounge and community ecosystem
The Partner Lounge creates space for collaboration with regional chapters and communities, including ISACA, ISC2, ISSA, Pacific Hackers, and CSA. BalkanID will provide an on-site videographer for practitioner spotlight interviews and selected conference coverage.
Meet Our Partners – don’t forget to enjoy spending some time with them during lunch and the fireside chat
- ISACA San Francisco
- ISACA Silicon Valley
- CSA San Francisco
- ISC2 North Bay
- ISC2 Silicon Valley
- Pacific Hackers
- ISSA
- AI University
Thank you to sponsors who will be appearing at the March 12th conference, The Debt Collector. We will see them there.
Oak is the AI-native Identity Operating System that rewires enterprise identity and access management. An AI connector framework reaches any application, whether on-prem, cloud, SaaS, or homegrown, then builds a live identity graph from raw evidence across every identity type, including the fast-growing population of non-human identities and AI agents. By mapping the access each identity holds against what it actually uses, Oak governs the full lifecycle of every identity with AI-built real-time risk decisions and root-cause remediation. Oak was founded by Shai Morag and Tal Marom and backed by a $60 million seed round from Greylock Partners, Accel, CRV, Hetz Ventures, and AlphaDrive Ventures.
Remember your option to pick up an additional CPE by enjoying the replay for HiddenLayer, Malcolm Harkins – Intezer, Mitchem Boles
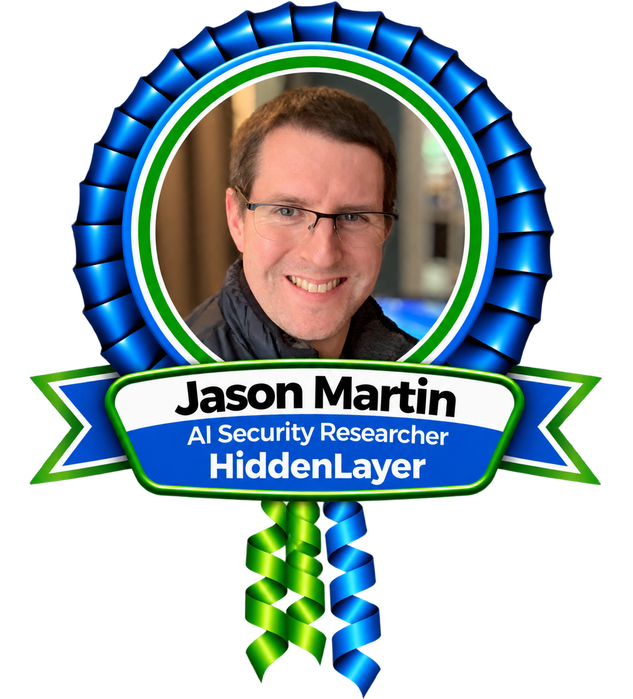
Unfortunately, Malcolm and Jason will not be available on the day, but we hope you enjoy one of several outstanding playback sessions from the recent ISC2 East Bay Conference library. HiddenLayer is working on sending us a subject matter expert. They are the keynote speaker at March’s conference, The Debt Collector.
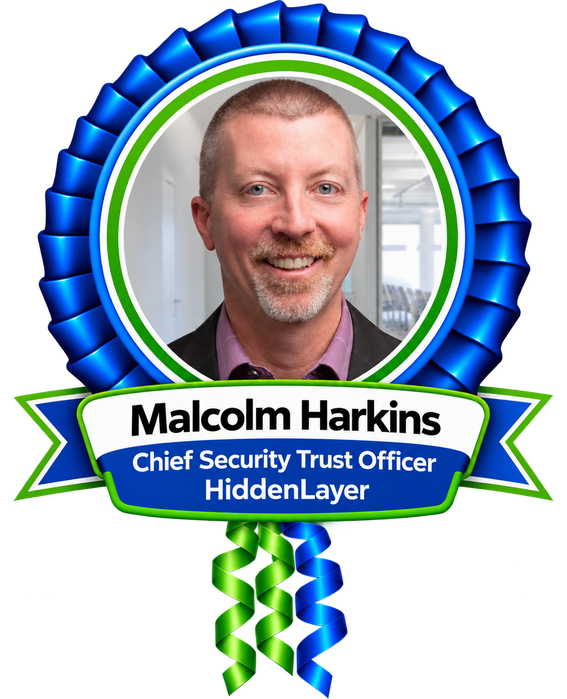
Malcolm Harkins is the Chief Security and Trust Officer at HiddenLayer, where he focuses on securing AI models and data. He previously held the role of Chief Security and Trust Officer at Cylance. Prior to that, he was the VP and Chief Security and Privacy Officer (CSPO) at Intel, leading the company’s security, privacy, and trust efforts. Malcolm is a respected voice on risk-based security and governance, promoting a balanced approach to managing risk, cost, and trust. He is an award-winning leader in the field of information security.
Malcolm won’t be present for this particular conference, but you can still view Malcolm’s Economic Impact of Securing AI keynote presentation from our March 2026 Conference.
Jason Martin is Director of Adversarial Research at HiddenLayer, where he explores how the latest AI security research intersects with practical application. Jason was amongst the earliest researchers to recognize the need for AI security, founding the Secure Intelligence Team in Intel Labs in 2016 to research AI security and privacy threats and defenses. For 20+ years, Jason has covered such diverse security topics as CPU microcode, authentication and biometrics, trusted execution environments, wearable technology, and network protocols, resulting in over 40 issued patents and several high-profile research papers in adversarial machine learning and federated learning. When he’s not working, Jason is either lost in the Pacific Northwest camping and hiking with his family, or he is lost in a technical project involving 3D printing, microcontrollers, or designing holiday lighting displays synchronized to music.
HiddenLayer (hiddenlayer.com) HiddenLayer’s AI Security Platform secures agentic, generative, and predictive AI applications across the entire lifecycle, including AI discovery, AI supply chain security, AI attack simulation, and AI runtime security. Backed by patented technology and industry-leading adversarial AI research, HiddenLayer protects IP, ensures compliance, and enables safe adoption of AI at enterprise scale.
Intezer – Playback Only – Enjoy CPE with Mitchem Boles
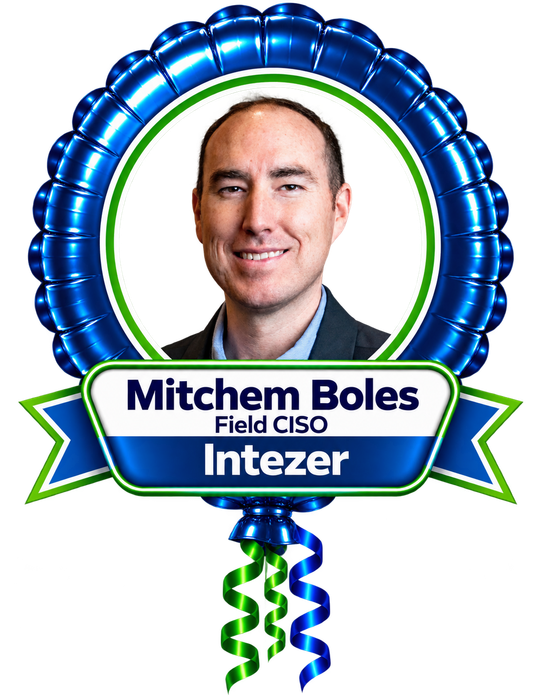
Mitchem Boles is an executive and strategic Field CISO for Intezer. His experience includes leading Information Security for a large healthcare network, directing Security Operations for a major U.S. electric utility, and roles in security leadership for energy & critical infrastructure, MSSP Services, and consulting. He is a graduate of Texas A&M University; certified CISSP, CCSP, and AWS; and his background of expertise includes: security strategy, SOC deployment, AI strategic implementation, security operations and staff development, tools differentiation, and risk management.
Watch Mitchem Boles’ presentation, AI-Adapted SOC Blueprint – A Practical & Strategic Framework, from the April 2026 member meeting.
Intezer (intezer.com) is the leading Autonomous SOC platform designed to emulate the decision-making process of a human security analyst at machine scale. By leveraging proprietary Genetic Malware Analysis, Intezer automatically triages, investigates, and responds to every alert originating from an organization’s existing security stack (EDR, SIEM, and Phishing reports). Unlike traditional automation that relies on rigid playbooks, Intezer’s AI-driven platform identifies the “DNA” of code to distinguish between trusted software, known threats, and sophisticated new mutations. This allows security teams to automate over 90% of their Tier 1 and Tier 2 monitoring tasks, effectively eliminating alert fatigue while ensuring that critical incidents are triaged and remediated in seconds rather than hours.
Corelight – Playback only – Working to confirm live session
Vern and Bernard have a tremendous track record speaking for our own and our local sibling chapters. We hope they can make it, but if they can’t, we have their best events on playback, and we hope you enjoy picking up some wisdom and CPE by giving them 45 minutes or more of your time.
Vern Paxson is a Co-Founder and Chief Scientist at Corelight, Inc., Professor of the Graduate School at UC Berkeley, and leads the Networking and Security Group at the International Computer Science Institute (ICSI). A deeply influential figure in internet security and measurement, he has contributed extensively to the IETF community, serving as chair of the Internet Research Task Force (IRTF) and as the IETF’s Transport Area Director.
An ACM Fellow and SIGCOMM Award recipient, Paxson is recognized for his groundbreaking work on internet measurement, intrusion detection, and large-scale attacks. He is the original author of the flex lexical analyzer and the creator of the Zeek intrusion detection system, which forms the foundation of Corelight’s Open NDR platform. His leadership has helped shape Corelight’s research direction and the evolution of Zeek for modern enterprise and cloud environments.
Watch Vern Paxson’s presentation on A Few Decades of Zeek and Network Monitoring from the June 2026 member meeting.
Bernard Brantley is the CISO at Corelight. He joined Corelight from Amazon, where he led threat hunting and intelligence for Amazon Consumer Payments. Previously, he was the architect behind network security monitoring for Microsoft’s High Value Asset (HVA) environments, including XboxLIVE. He serves as an advisor to several tech companies and is a participant in federal workshops on AI strategy. He attended the U.S. Military Academy at West Point.
Mike Henkelman is a Sr. Solutions Engineer for Corelight with thirty years of technical experience that includes building enterprise data centers and NOCs for ISPs, doing edge router and switch development for Cisco, and running the Vuln Management and FedRAMP IL5 programs for VMware. He frequently speaks at conferences such as DefCon and B-Sides.
Corelight (corelight.com) is the pioneer and fastest-growing provider of Open Network Detection and Response (NDR), delivering a unique approach to cybersecurity risk centered on comprehensive network evidence. As the only solution powered by the dual open-source foundations of Zeek® and Suricata—now enhanced by GenAI—Corelight provides deep visibility into network traffic by transforming raw data into high-fidelity logs, metadata, and actionable insights. By equipping elite defenders at the world’s most mission-critical enterprises and government agencies with this rich evidence, the platform enables rapid threat hunting, forensic analysis, and complete situational awareness across complex, distributed environments. Ultimately, Corelight helps security teams level up their defenses, accelerating investigations and dramatically reducing the time required to detect and neutralize sophisticated attacks and model theft.
Veria Labs
Veria Labs (verialabs.com) provides an AI-native offensive security platform designed for autonomous vulnerability discovery and exploitation. Founded by members of the #1 US competitive hacking team, Veria Labs builds specialized AI agents that integrate directly into Git repositories and CI/CD pipelines to analyze codebases continuously. These agents operate faster than human researchers, finding deep, complex vulnerabilities that traditional tools miss and generating real-world exploit PoCs to verify risk and eliminate false positives. By adapting to business logic and providing automated remediation, Veria Labs shifts offensive security left, enabling organizations to validate their security posture and secure critical vulnerabilities with high confidence and at machine speed.
Book your group rate for the ISC2 East Bay Chapter Room Block